

House Committee Probing Auto Cybersecurity
The U.S. House Energy and Commerce Committee has posed a series of questions to 17 automakers, in hopes of evaluating the auto industry’s ability to mitigate cybersecurity threats.
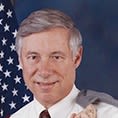
UPTON
UPTON
Members of the U.S. House Energy and Commerce Committee last week sent letters to 17 automakers, requesting information about the auto industry’s measures to address cybersecurity challenges as vehicles become more connected.
The May 28 letters express concerns about the potential for hackers to assume control of vehicle systems over the Internet. The letters also urge the industry and the National Highway Traffic Safety Administration to work together to develop strategies to mitigate any growing risks.
Committee members also sent a letter to NHTSA Administrator Mark R. Rosekind, asking for details about the agency’s means for evaluating, testing and monitoring potential cyber vulnerabilities.
“Connected cars and advancements in vehicle technology present a tremendous opportunity for economic innovation, consumer convenience, and public health and safety,” the letters state. “These benefits, however, depend on consumer confidence in the safety and reliability of these technologies. While threats to vehicle technology currently appear isolated and disparate, as the technology becomes more prevalent, so too will the risks associated with it. Threats and vulnerabilities in vehicle systems may be inevitable, but we cannot allow this to undermine the potential benefits of these technologies.”
The letters to automakers and NHTSA pose a series of questions and request responses by June 11. Rep. Fred Upton (R-Mich.) chairs the House Energy and Commerce Committee.
Some of the questions posed to the automakers include:
What are the greatest challenges to cybersecurity in the automobile industry?
What policies, procedures, and practices do you employ to evaluate potential cyber vulnerabilities during the design, implementation and testing of vehicle components or technology?
Who within your organization structure is responsible for evaluating, testing, and monitoring potential cyber vulnerabilities in your products?
How do you work with suppliers to minimize, evaluate, and address potential vulnerabilities in the supply chain?
What steps have you taken to evaluate how connected elements, such as in-vehicle Wi-Fi and infotainment services, connect to or interact with vehicle safety systems and/or functions?
How is the automobile industry working with the federal government to address the challenge of cybersecurity?
The letters were mailed to General Motors, Ford, FCA US, Toyota, Honda, Nissan, Hyundai, Mazda, Mitsubishi, Kia, Subaru, Mercedes Benz, Volvo, Volkswagen, Audi, Porsche and Tesla.
To view copies of the letters, click here. To view a Consumer Reports video about NHTSA's efforts to prevent cybersecurity threats, click here.
More Safety
Nexar-Nauto Merger Aims to Give Fleets Better Safety Intelligence Through Larger Driving Dataset
Stefan Heck tells Automotive Fleet that combining more than 10 billion miles of driving history with Nexar's AI models will give fleets deeper insights into driver risk and roadway conditions than either company could provide independently.
Read More →
Don't Wait for a Crisis: 5 Ways to Build Mental Health Into Your Fleet Safety Program
For Suicide Prevention Month, fleet and safety leaders have an opportunity to put mental health where it belongs: at the center of workplace safety.
Read More →
How Camera Data Can Strengthen a Fleet’s Insurance Renewal
Insights from a commercial insurance carrier and a broker show how fleets can turn video telematic data, driver coaching, and improved claims results into a stronger case at insurance renewal.
Read More →
The Safest Fleets Aren’t the Ones with the Most Technology
You’ve made the telematics investment. Here’s how to capture the other half of its value and build the safest fleet on the road.
Read More →
Hidden in Plain Sight: Fleet Compliance Risks
Fleet compliance isn't just about having policies — it's about consistently enforcing them. This practical guide reveals six hidden compliance risks common in public sector and shared fleet operations and outlines proven strategies to improve visibility, accountability, and audit readiness
Read More →
NETS Sets 2026 Fleet Safety Benchmark Conference for Indianapolis
The Sept. 15–17 program will feature fleet benchmarking data, case studies, emerging technologies, and implementation strategies while running alongside the NSC Safety Congress & Expo.
Read More →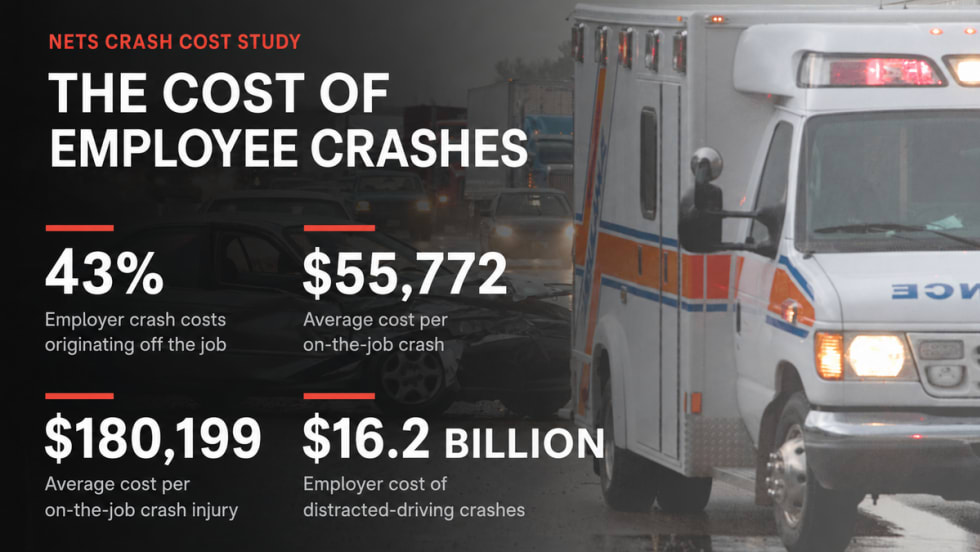
Off-the-Job Crashes Account for 43% of Employers’ $61.7 Billion Crash Burden
NETS quantifies costs dispersed across fleet, risk, HR, and other departments while providing new per-crash benchmarks for employers.
Read More →
Ram Recalls More Than 1.27 Million 1500 Pickups for Seat Belt Anchor Issue
The recall affects certain 2019-2026 Ram 1500 pickups that may have improperly attached second-row seat belt buckle anchors.
Read More →
How Better Visibility Cut Speeding Violations by 48%
Fleet leaders don't need more data, they need clearer visibility into what the data is saying. This case study explores how one utility replaced speeding-event counts with a single metric — miles driven in violation — to strengthen safety and significantly reduce speeding violations.
Read More →
Operation Safe Driver Week: Why the Industry's Oldest Safety Campaign Still Matters to Fleets
A look at how a 2007 enforcement initiative became one of the most consequential weeks on the fleet safety calendar, and what it means for your drivers in 2026.
Read More →